Security and User Settings
Managing your app users’ roles, permissions, and security settings can be done from your QuickConnect Portal.
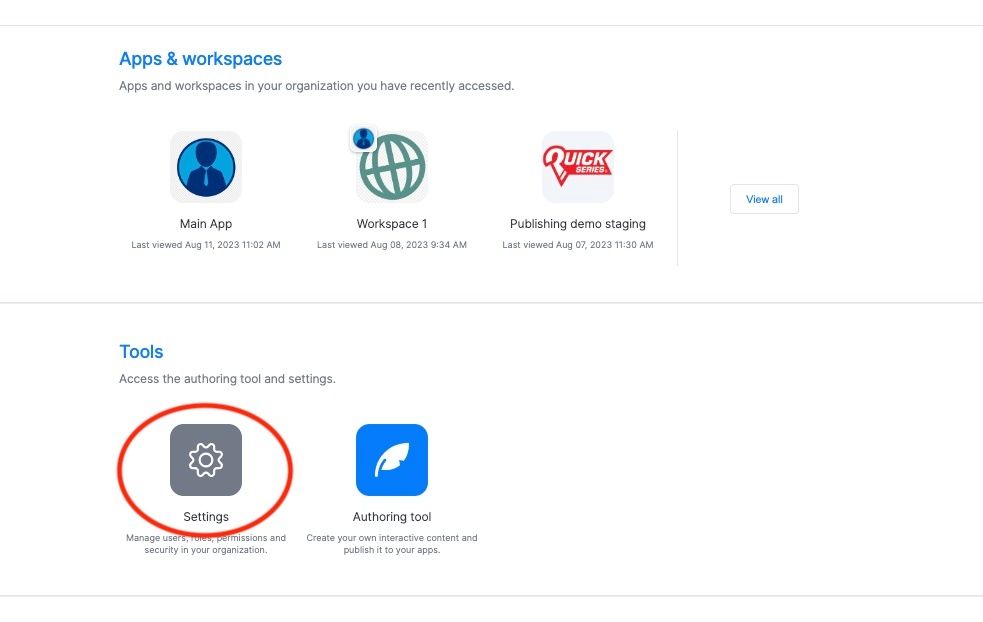
From the portal home screen, click on Settings at the bottom of the page.
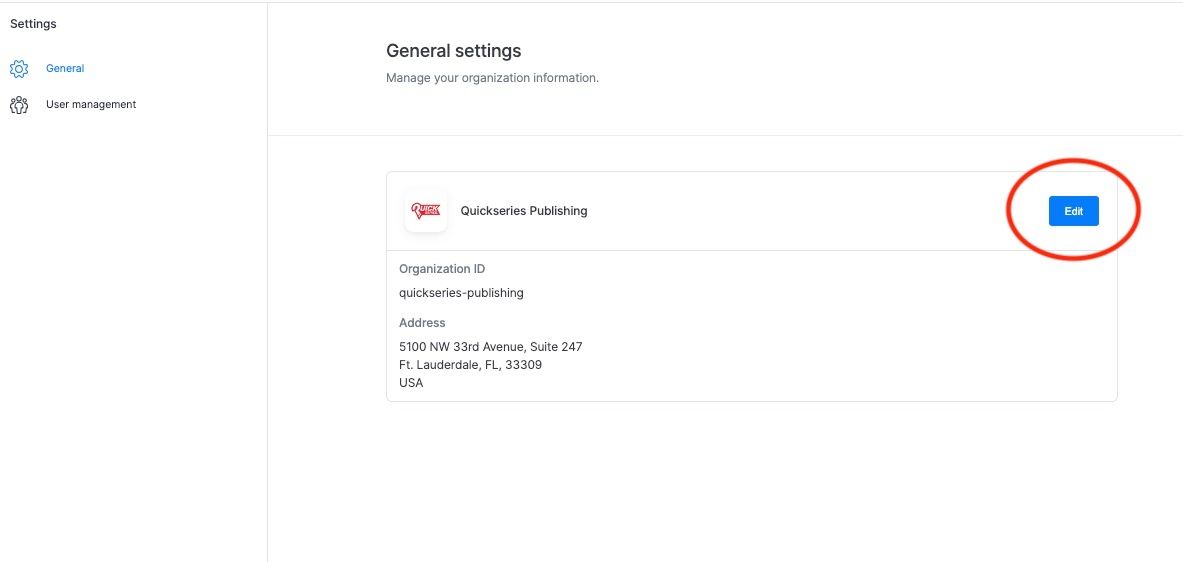
First – let’s look at the General Settings where you can edit your organization’s details.
Click on Edit at the top right to make any changes to your organization details in the portal.
You can change the logo that appears at the top of your portal home page by clicking on replace.
Additionally, you can change your organization name and slug. Please note: making these changes will affect the base URL of the portal and will change the organization ID required to log in to the portal.
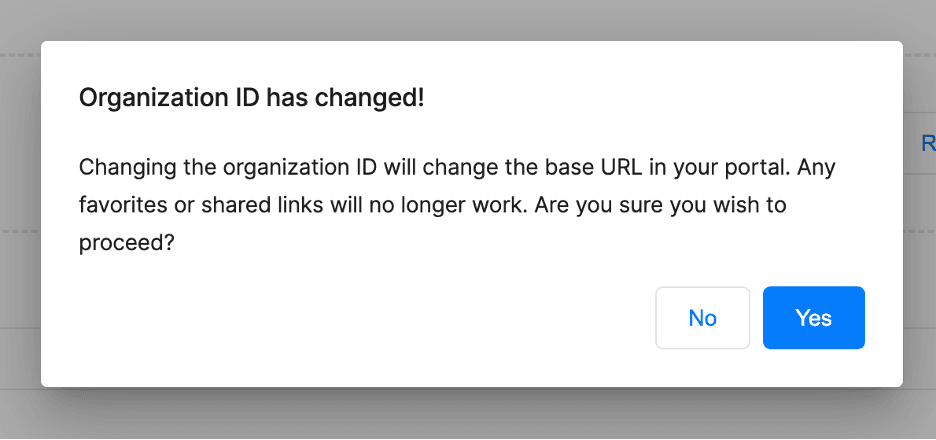
Lastly, you can add or change the organization address. This address is used by the privacy policy editor when using a placeholder. Click here to find out more.
When you are finished making changes, click on the SAVE button at the top right of the page to commit the changes.
User Management
Next, let’s explore the User Management section by clicking User Management in the left-hand menu.
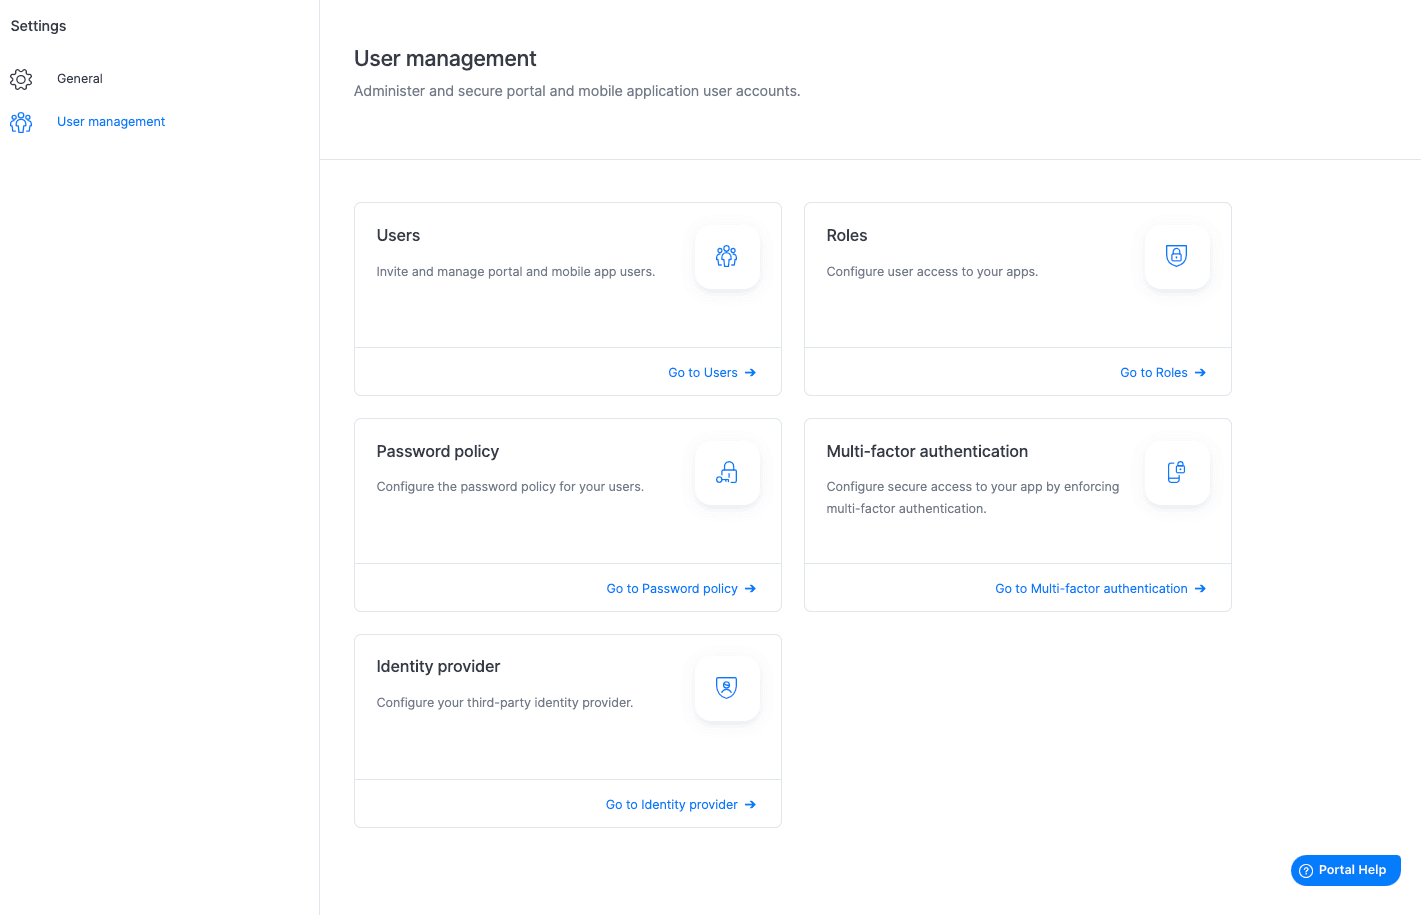
The user management page allows you to manage and invite portal and app users, configure your third-party identity provider, set a password policy, configure your multi-factor authentication, and define Roles and Permissions for users.
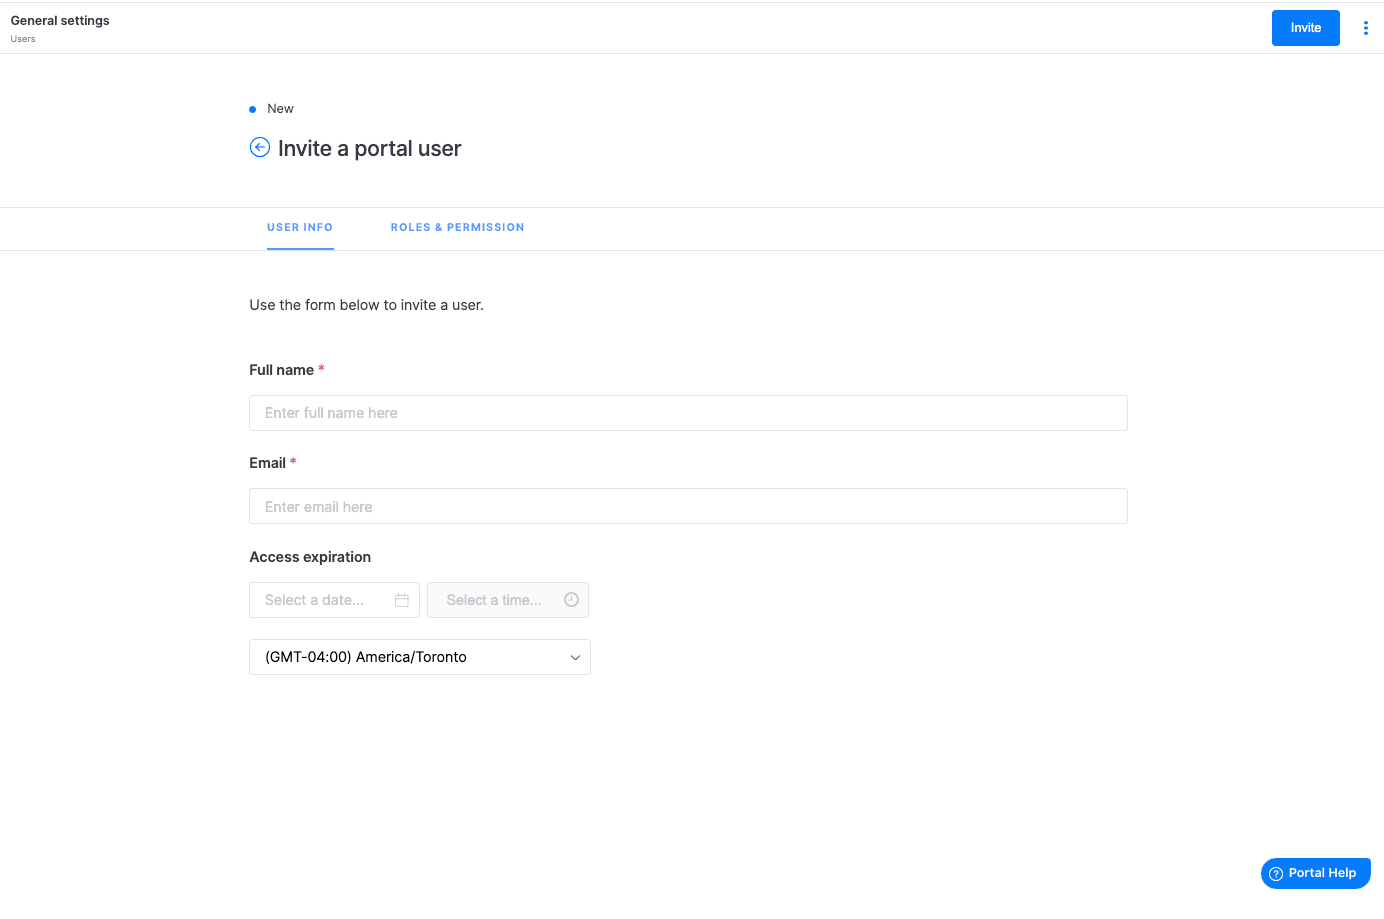
You can invite a new user by clicking on the +Invite link on the right. This will prompt you to add the user’s full name and email address (at the minimum) and define user access, roles, and permissions.
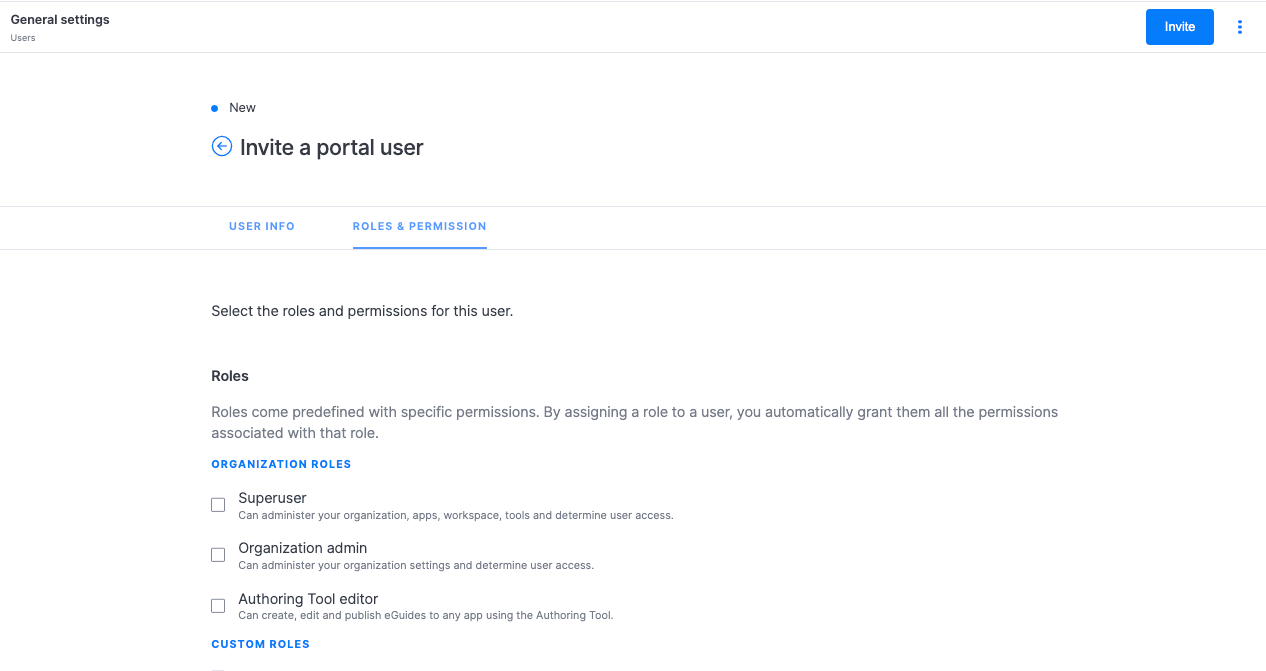
You can select the predefined Role and Permissions, or create and assign custom roles to grant users the permissions associated with those roles.
Once you are done, click on the Invite button at the top right to invite your portal user.
The user will receive an email from noreply@quickseries.com informing them that they have been invited to the app organization and asking them to up their account (password and Multi-Factor Authentication).
On the portal user’s main page, you can view which user invites are pending and which have been activated.
Right-clicking on a selected user allows you to resend the invite to all pending users, resend the invite to only the selected user, edit user details, view the user details, or delete the user.
For more details on how to manage and control who connects to your portal and app, visit the User Management Page.
Roles
On the main User Management page, click on Roles to configure user access to your apps.
Default Roles
- SuperUser: Manages their organization, applications, workspaces, and tools. They have full control over who gets access to what.
- Organization admin: Manages organization settings and determines user access.
- Authoring tool editor: Creates, edits, and publishes eGuides to any mobile app using the Authoring Tool.
Default Permissions
Each app has the following three default permissions:
- Admin: View, create, read, update, and delete content and administer settings.
- Editor: View, create, read, update, and delete content.
- Viewer: View private content in the mobile app.
You can also create custom roles with specific permissions.
Click on Create to see the configuration options, set up your Roles and Permissions, and save.
Password Policy
On the main User Management page, click on password policy to configure your password policy for portal users.
You can set the level of password protection for new accounts and resetting Portal passwords by clicking on edit on the top right of the screen.
You can optionally:
- Set a minimum password length
- Require at least one uppercase letter
- Require at least one lowercase letter
- Require at least one number
- Require at least one non-alphanumeric character
Click Save at the top right once you are done editing your password policy.
Multi-Factor Authentication
On the main User Management page, click Multi-factor authentication to configure user access to your apps.
Selecting multi-factor authentication (MFA) will enforce secure access to the app.
Click on Edit to switch from Optional MFA to Required MFA.
Identity Provider
Third-party identity providers are external services that manage user authentication. They allow users to sign into multiple applications using just one set of credentials.
Back on the main User Management page, click the Go to Identity Provider button to configure an Identity Provider (IdP).
Click the Edit button to see the configuration options. We offer three ways to connect your IdP:
- Google Workspace
- OpenID Connect (OIDC)
- SAML
Each has different requirements and you may want to seek help from your IT department to configure them correctly.
The Provider name input will determine the label of the login button on the login page.
Click Save to activate the IdP authentication.
You can test the configuration by logging out and clicking the IdP button that will appear in the normal email + password form.
This will redirect you to the IdP login page, and then to your organization’s App Launcher page, if successful.